Weekly ecommerce tips, deals & news.
An account takeover is when someone signs in to a real customer’s account and uses it as their own. Nothing is hacked in the way people picture. The password was simply correct. Your store has no reason to think anything is wrong.
An account takeover happens because passwords travel. A customer uses the same one on a dozen sites, and one of those sites leaks it. Your store then receives a perfectly valid sign in.
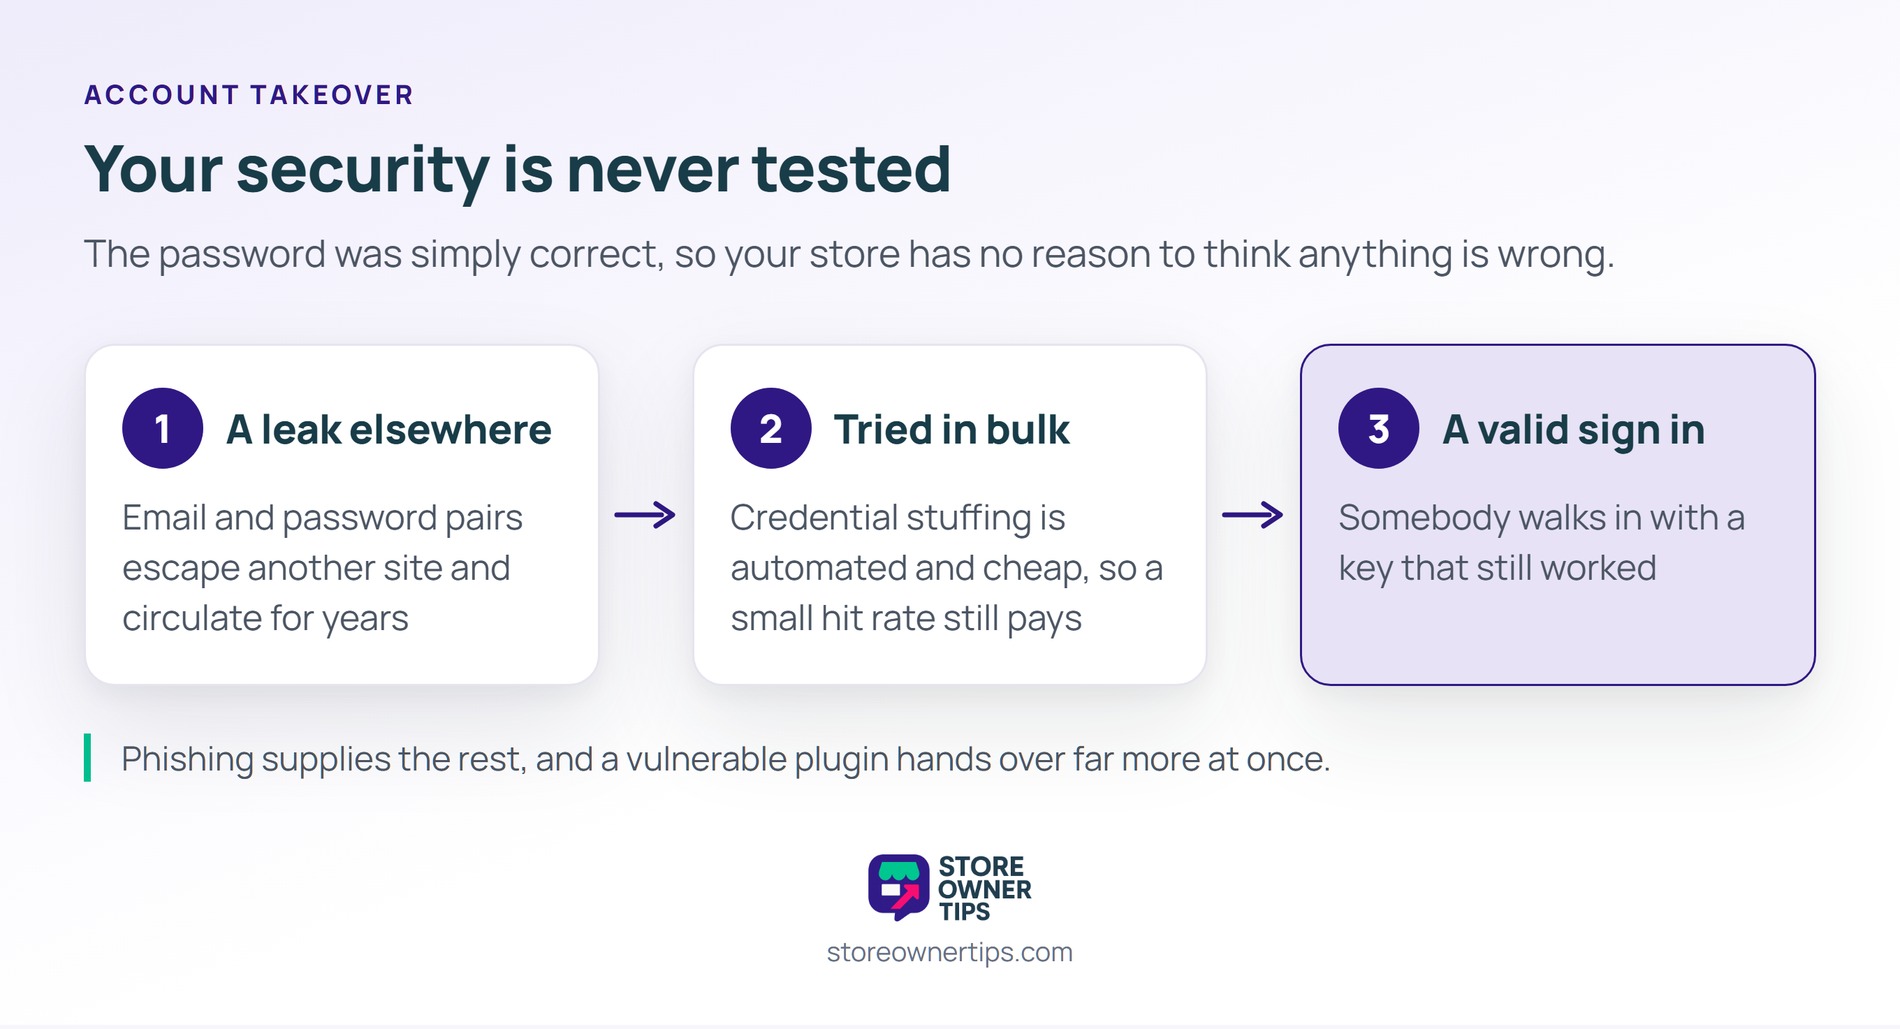
Your security was never tested. Somebody just walked in with a key that still worked.
Most come from breaches elsewhere. Lists of email and password pairs circulate for years after the site they came from was fixed.
Attackers then try those pairs against other sites in bulk. The practice is called credential stuffing, and it is automated and cheap. A small hit rate is still profitable at that volume.
Phishing supplies the rest. A convincing email asks a customer to sign in, and the page collecting the password is not yours.
There is a route through your own site too. A vulnerable plugin can expose sessions or user data directly. That is rarer, and it hands over far more at once.
The first move is usually quiet. They change the delivery address and leave everything else alone. A saved card then pays for goods going somewhere new.
Stored value is the second target. Loyalty points, store credit and gift balances all spend like money and rarely trigger a check.
Some take the data instead. Order history holds names, addresses and partial card details, which are useful elsewhere.
The email change is the one that hurts. Once the address on file is theirs, your password reset no longer reaches the real customer.
None of this looks urgent in your admin screen. Each action is something a genuine customer does from time to time.
A retail account buys one order on one card. A wholesale account is a different proposition entirely.
It carries approved pricing, so goods can be bought well below the public rate. It often carries payment terms as well, which means no card is needed at all.
Order sizes make it worse. Nobody questions a trade account ordering forty units, because that is what trade accounts do.
So the checks belong at the start, where you decide who gets an account. Wholesale Suite covers that step in its guide to wholesale customer onboarding.
The stock is the obvious loss and rarely the largest one. Goods shipped on a stolen login are gone, with no card to dispute.
The customer relationship is the expensive part. You now have to tell a good account that their details were used against them. Many of them quietly stop ordering afterwards.
Then there is the cleanup nobody plans for. Resetting affected accounts, reviewing recent orders, and answering worried customers takes days rather than hours.
A trade account adds one more layer. An unpaid invoice on stolen goods becomes a collections problem against a customer who owes you nothing.
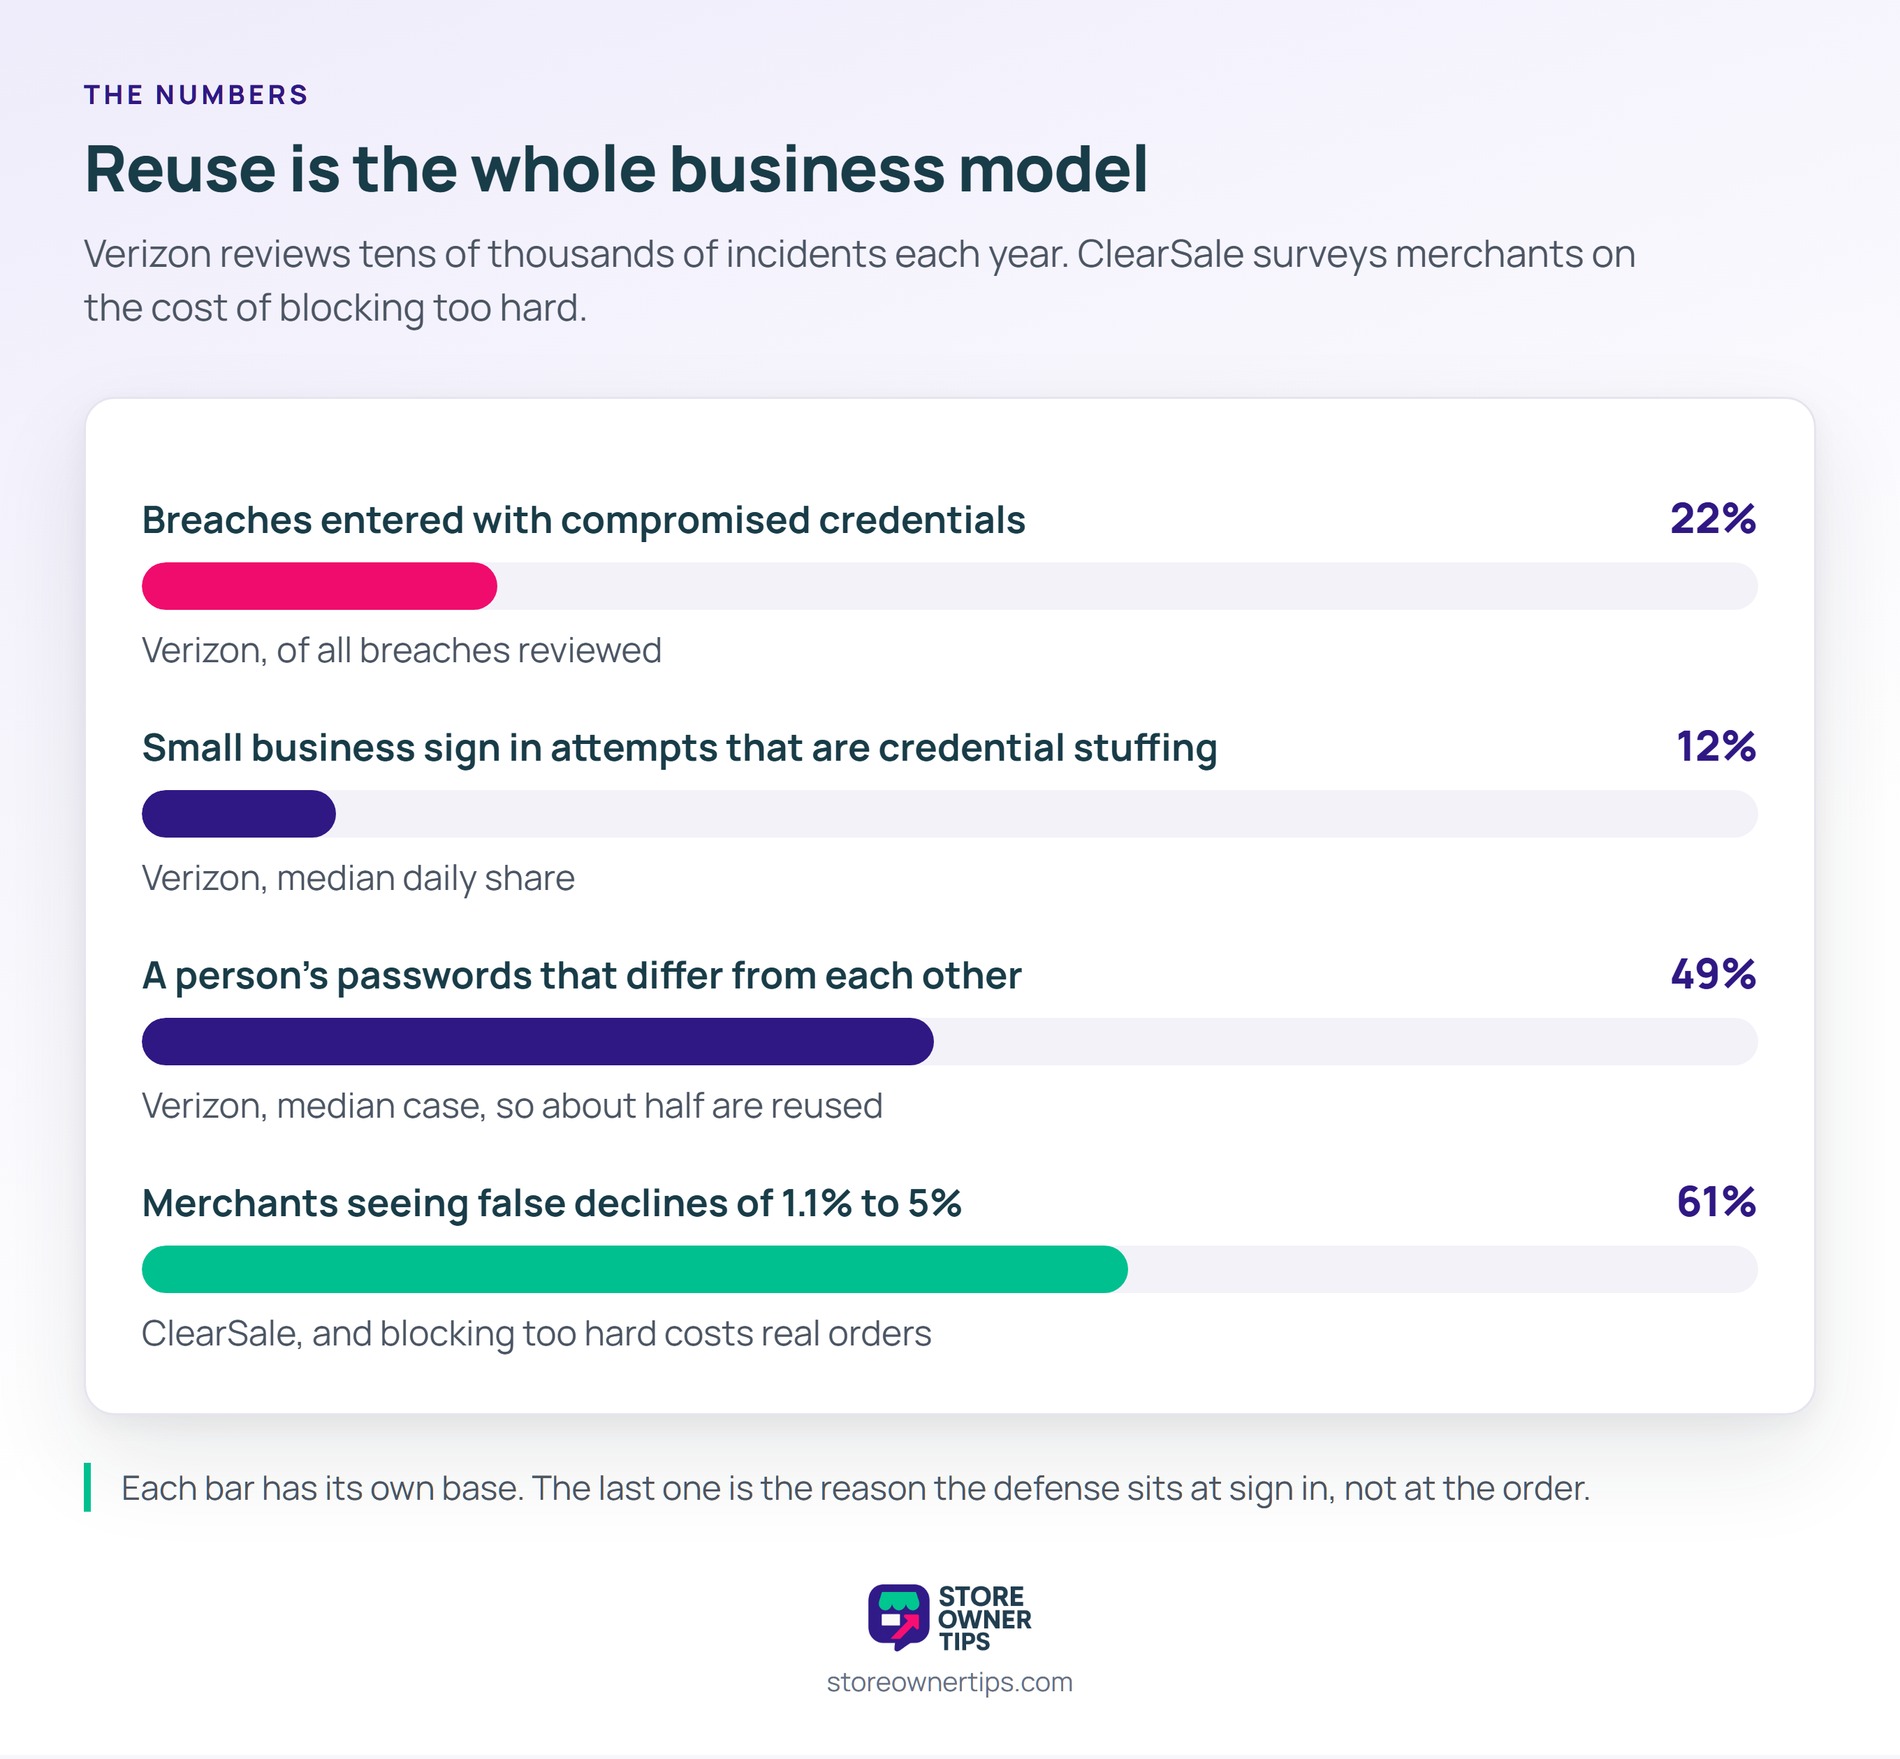
Stolen logins are now one of the most common ways in anywhere. Verizon reviews tens of thousands of incidents for its annual breach report.
It found compromised credentials were the way in for 22% of the breaches reviewed. At small businesses, credential stuffing accounted for 12% of all sign in attempts.
The same research explains why it works. In the median case, only half of a person’s passwords differed from each other. Reuse is the whole business model.
Your plugins matter here as well. Patchstack counted 11,334 new WordPress vulnerabilities in a year, with 46% unpatched at disclosure.
Overreacting has a price too. ClearSale reported that 61% of merchants see false decline rates between 1.1% and 5%. Blocking too hard costs real orders.
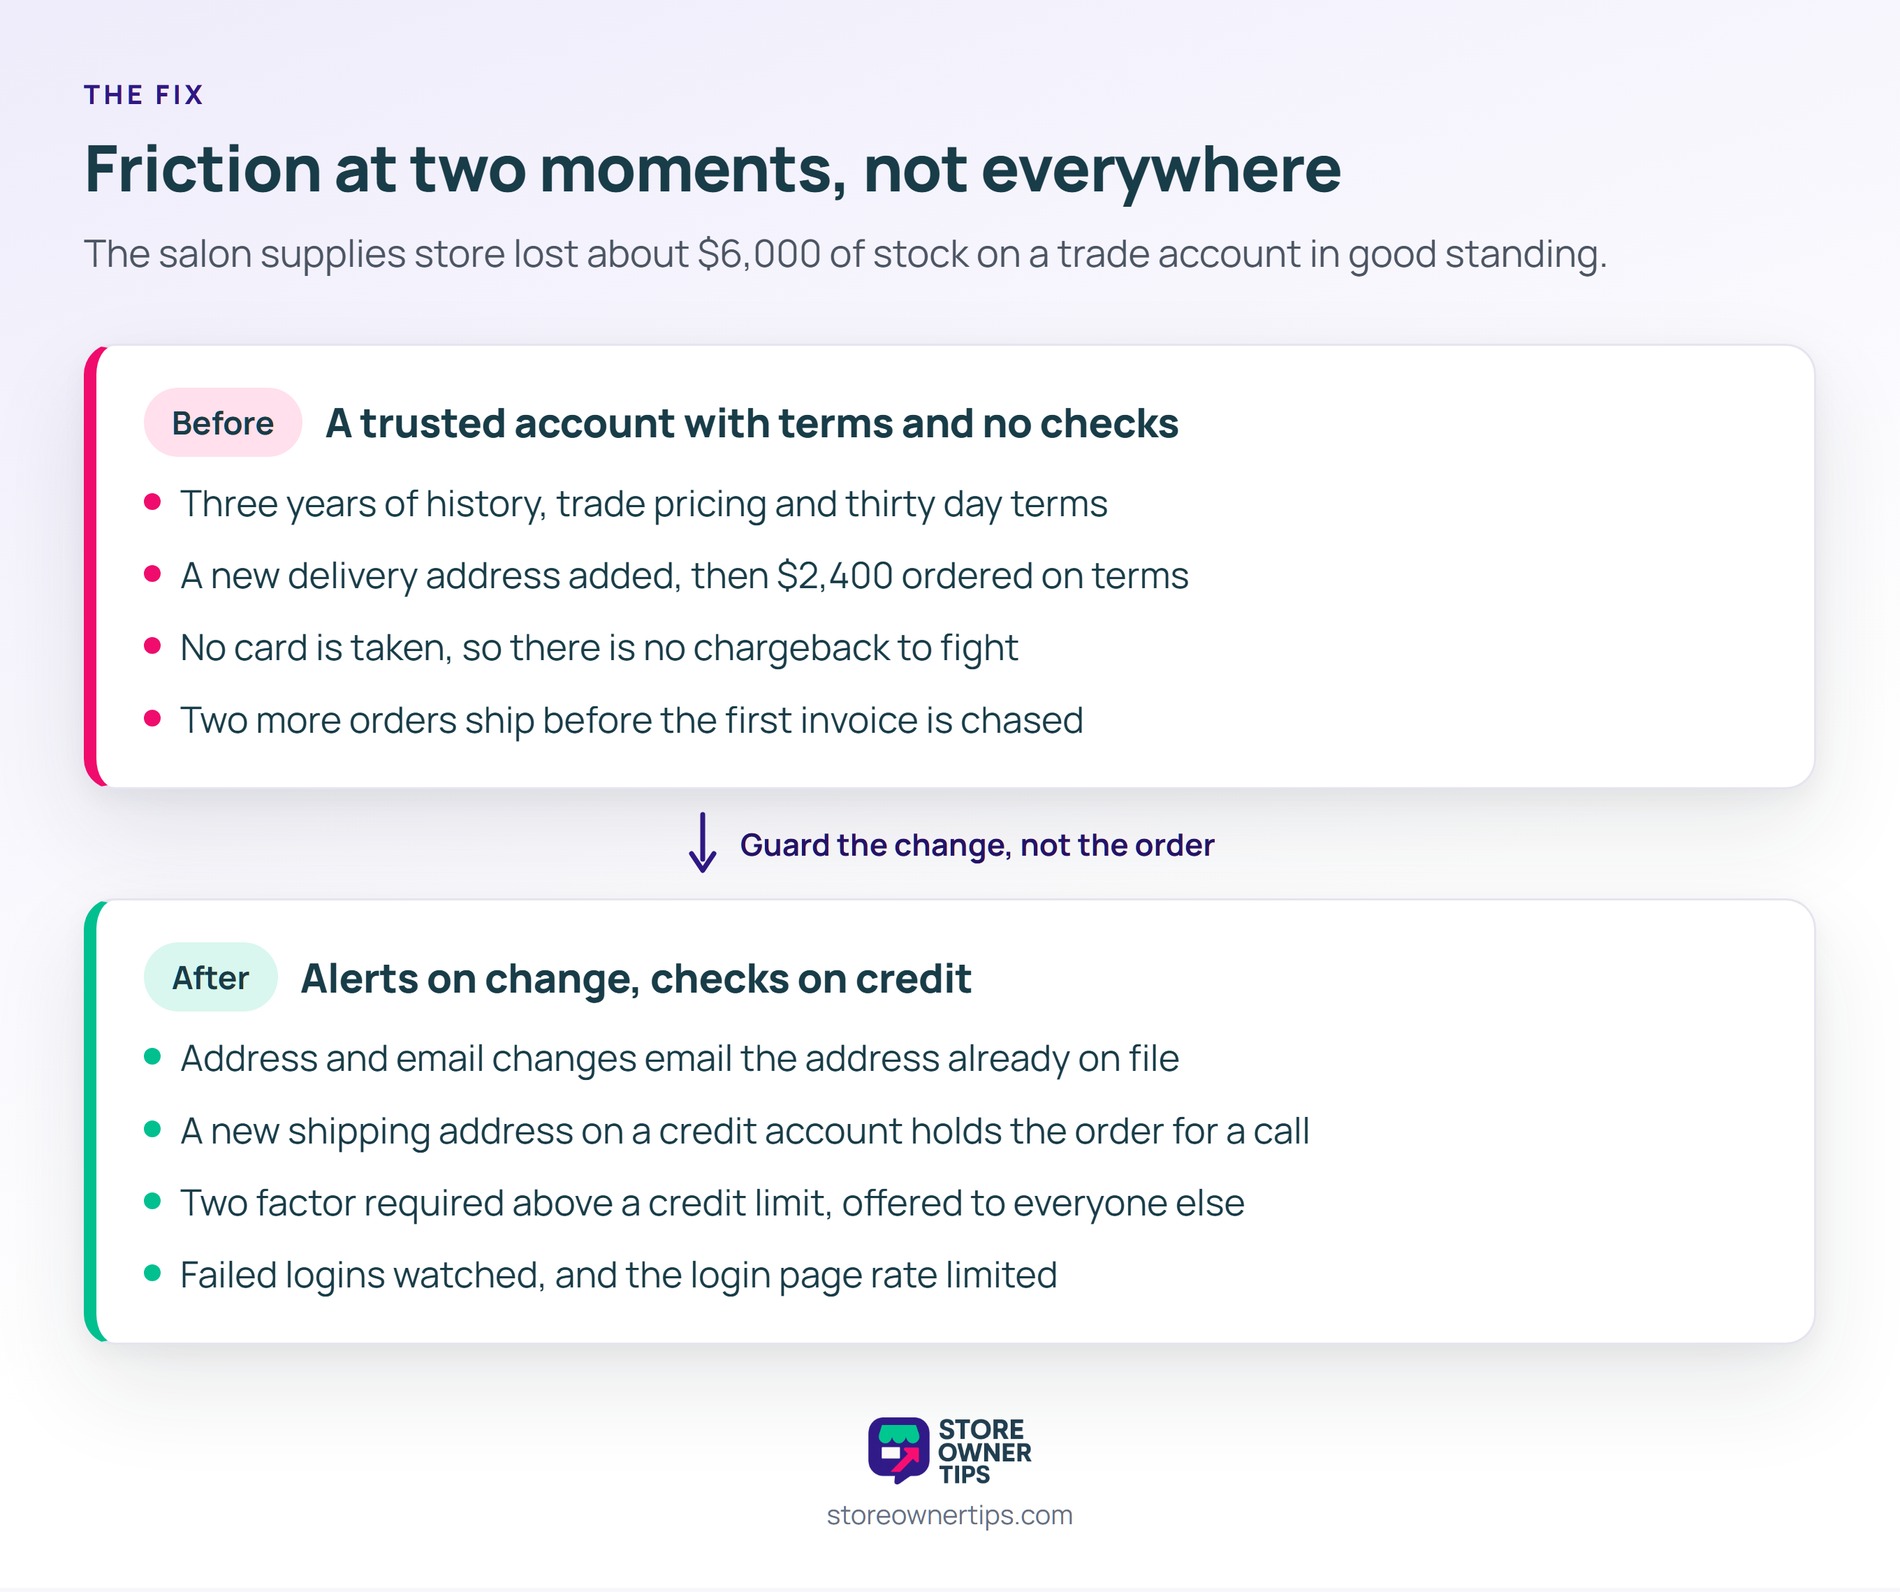
An account takeover looks like a good customer behaving slightly oddly. Here is a hypothetical example. Imagine a store selling salon supplies to both the public and the trade.
In this scenario a salon has held a wholesale account for three years. It gets trade pricing and thirty day payment terms. Orders arrive most months without anyone reviewing them.
The salon owner uses the same password on several sites. One of those sites is breached in the spring.
In June someone signs in to the trade account successfully. They add a new delivery address and place an order for $2,400 on terms. No payment is taken at checkout.
Everything about it looks normal from the inside. A known account, trade pricing, a plausible order size, and an invoice due in thirty days.
Two more orders follow over the next fortnight. The goods ship each time, because the account is in good standing.
The real salon finds out when the first invoice is chased. Roughly $6,000 of stock has gone, and the store carries the loss. There is no card to dispute and no chargeback to fight.
So the store adds friction at exactly two moments. Changing a delivery address now sends an email to the address already on file. Changing the account email does the same thing.
Next, orders on terms get one check. A new shipping address on a credit account holds the order for a phone call. That call takes two minutes.
Two factor sign in is offered to every trade customer and required above a credit limit. Retail customers are left alone, since their accounts carry far less.
The store also writes down what happens next time. Who freezes the account, who calls the customer, and who checks the last month of orders. Deciding that during an incident wastes the hours that matter.
Finally the store watches failed logins. A spike of failures across many accounts is credential stuffing in progress. Rate limiting the login page stops most of it.
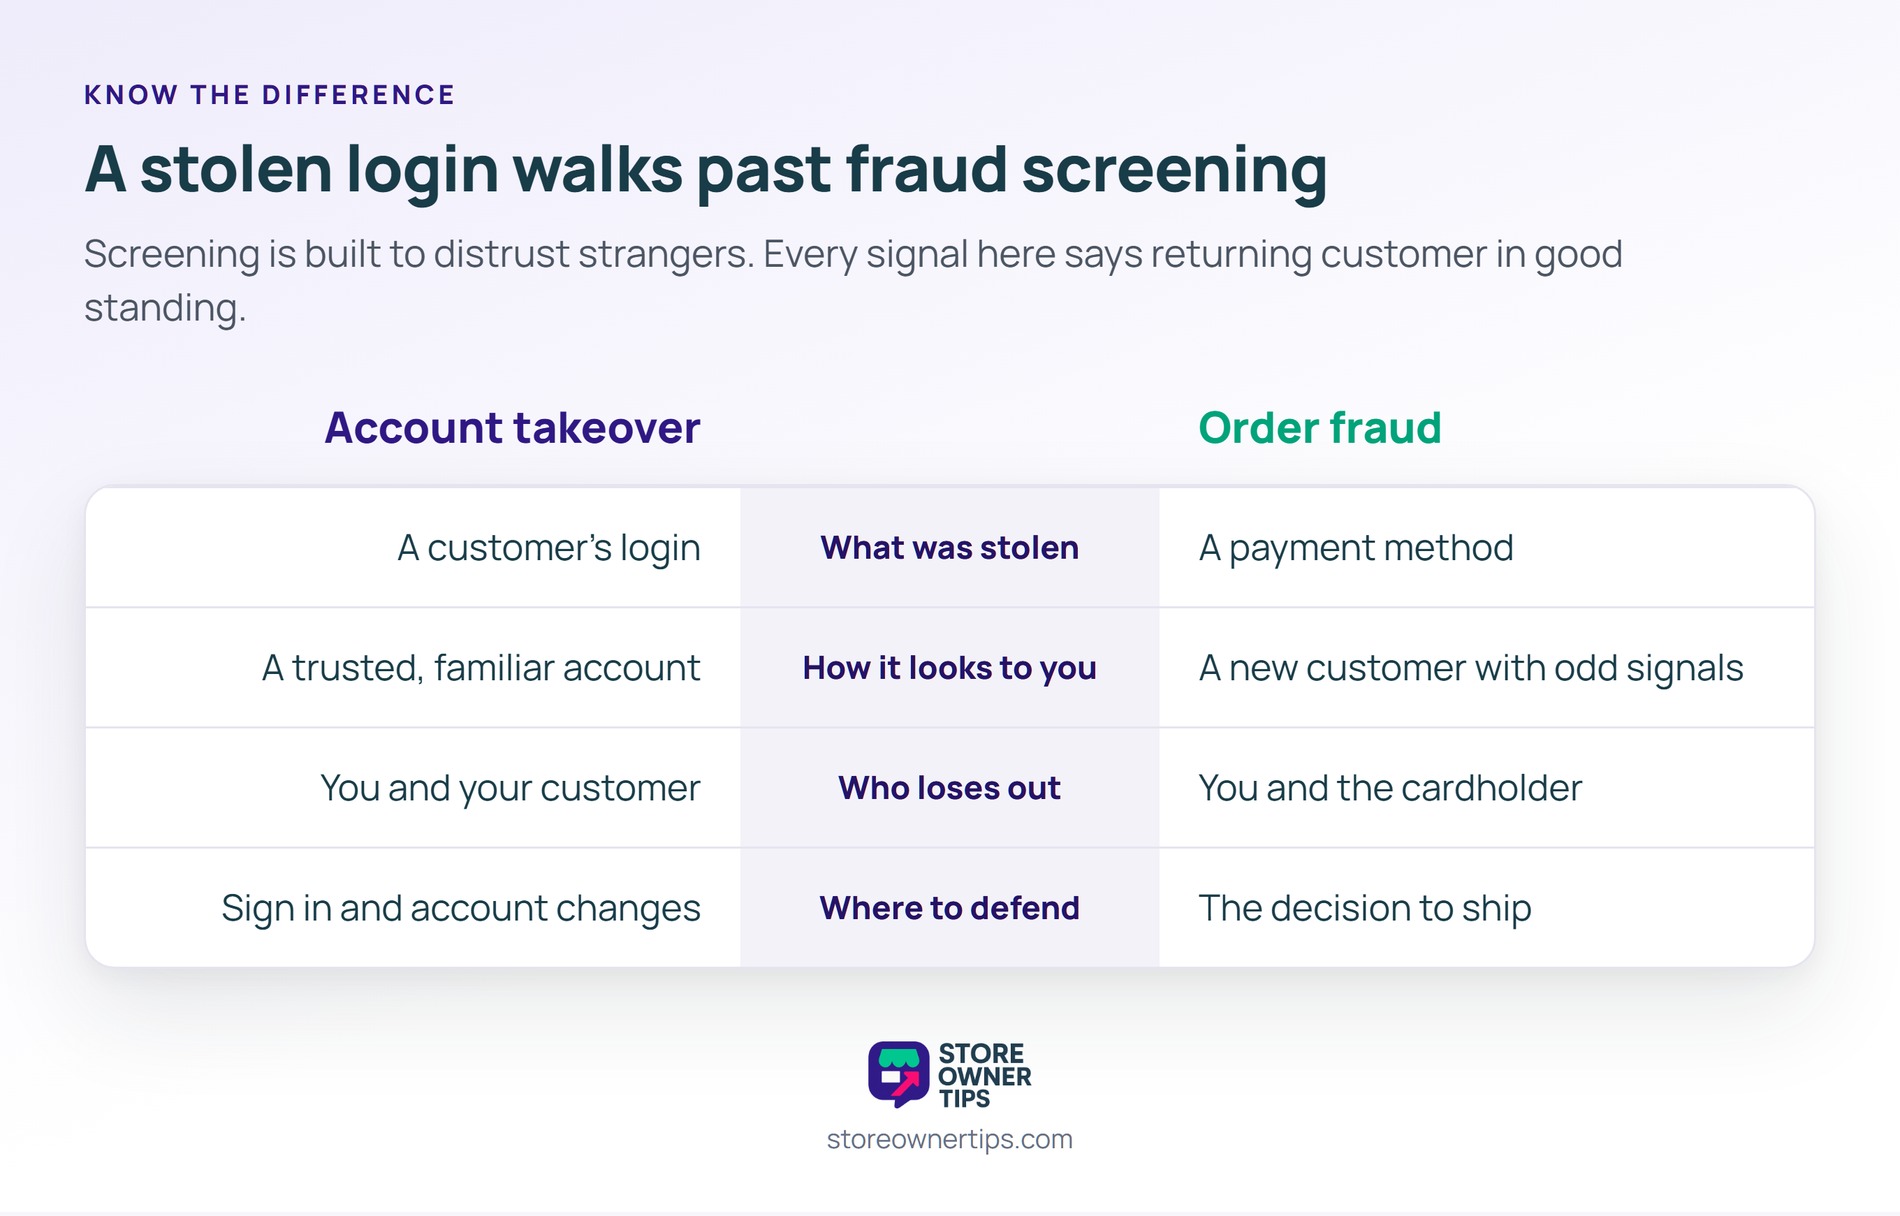
| What you’re comparing | Account takeover | Order fraud |
|---|---|---|
| What was stolen | A customer’s login | A payment method |
| How it looks to you | A trusted, familiar account | A new customer with odd signals |
| Who loses out | You and your customer | You and the cardholder |
| Where to defend | Sign in and account changes | The decision to ship |
Fraud screening is built to distrust strangers, which is why a takeover walks past it. Every signal it reads says this is a returning customer in good standing. The defense has to sit earlier, at the sign in and at the account change. By the time the order exists, it looks like your best kind of order.
Look for a change followed quickly by an order. A new delivery address, a new email, or a password reset just before checkout is the pattern.
Failed login spikes are the earlier warning. Many failures across many accounts means somebody is testing a list.
Match the requirement to what the account can spend. A retail account with no saved card is a poor target.
Require it where value sits, which usually means trade accounts and stored credit. Offer it to everyone else without forcing it.
The leak is not yours, and the loss still is. Goods shipped on a stolen login come out of your stock.
That is why the controls worth having are yours to set. You cannot fix other people’s breaches, and you can notice a strange address change.
An account takeover matters because it turns your trust into the weapon against you. The better the customer, the less scrutiny their orders get. In short, the accounts you check least carefully are the ones worth stealing most.
Copyright © StoreOwnerTips.com. All Rights Reserved.
